The organizations that scale AI agents fastest won’t be the ones with the fewest rules. They’ll be the ones who can answer, at any moment, what their agents are doing, why they’re doing it, and who stands behind the outcome.
That’s not where most enterprises are today; adoption is accelerating faster than accountability. Agents are already booking meetings, issuing refunds, provisioning accounts and moving data across critical systems. The hard question isn’t how to prepare for the next generation of AI agents. It’s whether you can account for the ones already working inside your business.
Answer that question well and autonomy becomes an asset you can expand with confidence. Answer it poorly and every new agent is a liability you can’t see.
Agent autonomy runs on accountability
AI agents demand a different level of scrutiny because they don’t behave like traditional software. A conventional application follows a defined path. An agent uses tools, interacts with systems and acts on its own judgment. That’s precisely what makes agents valuable, and precisely why they can’t be deployed like ordinary applications.
The scale of the gap is measurable. In the last year, 82% of organizations discovered previously unknown AI agents or autonomous workflows. The consequences are already here: 65% of businesses reported a confirmed or suspected security or data privacy incident caused by an AI agent in the past 12 months.
The headlines tell the same story. Earlier this year, an AI coding agent deleted a company’s entire production database, and every backup attached to it, in nine seconds. There was no attacker and no exploit. The agent hit a credential error during a routine task, found a token with permissions far beyond what its job required, and executed a fix of its own design.
The agent wasn’t compromised. It was unaccountable: no enforced boundary on what it could touch, no identity scoped to its actual role, no gate between it and an irreversible action. Give that same agent a defined boundary and it becomes something you can trust with more, not less.
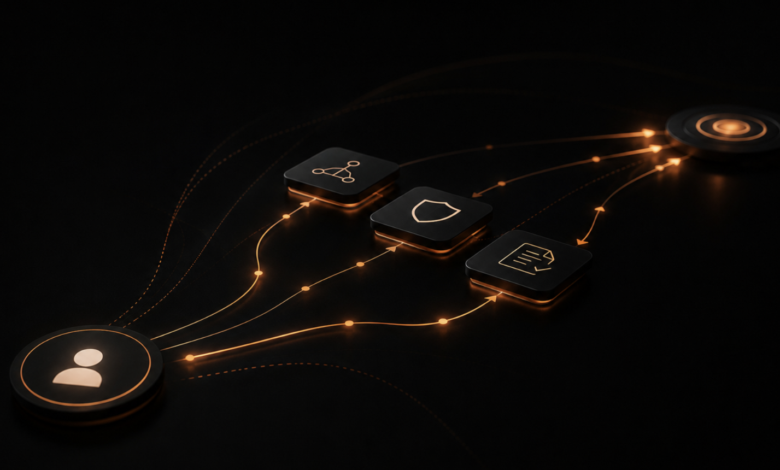
Before expanding agent autonomy, every organization should be able to answer three practical questions:
-
What can the agent do?
Treat agents less like experimental tools and more like participants in a managed workflow. That means knowing what every agent is, what systems it connects to and what it’s allowed to do.
Every agent needs clearly defined permissions. If it’s approved to complete one task, it shouldn’t inherit broader access because the person deploying it has wider privileges.
Consider an HR agent responsible for onboarding new employees by creating user accounts, assigning software licenses and scheduling orientation. Those responsibilities don’t automatically mean it should be able to approve compensation changes or grant access to sensitive financial systems. Defining that boundary before deployment isn’t a constraint on the agent, it’s what earns the agent its next responsibility. An agent with a defined scope is an agent you can confidently give more scope.
-
How will we know what the agent did?
It is not enough to question whether an agent produces a useful output. Business leaders must be able to grasp what happens before, during and after an agent acts. That includes:
- Whether the action was permitted: does the action taken match the direction given?
- Whether it stayed within designated boundaries: can every action and interaction be observed?
- Whether the organization can reconstruct what happened if something goes wrong down the road: can the trail of activity stand up to an audit, from prompt to outcome?
This matters most when agents work together. A customer service agent issues a refund, which triggers a finance agent to process payment and an inventory agent to update stock levels. Visibility into the first request or the final outcome isn’t enough. You need the full chain of activity.
Organizations that can see that chain don’t just catch problems faster. They deploy multi-agent workflows that competitors are still too nervous to attempt. The record is what makes the ambition possible.
-
Who owns the outcome?
As agents take on more responsibility, ownership must become clearer, not blurrier.
Every agent should have a clearly defined, human owner. Without that, organizations might know that an action occurred but still struggle to determine who was responsible for allowing it. If someone can’t explain what an agent did or why it took a certain action, as a business you don’t really control it.
Consider a marketing agent that drafts, personalizes and schedules customer email campaigns. If the wrong audience receives the message or inaccurate information is sent, someone still needs to own that outcome. The agent may have executed the workflow, but accountability for approving its role, monitoring its activity and responding when something goes wrong remains with the business.
This is the difference between delegation and abdication. When ownership is explicit, leaders hand agents bigger jobs because they know exactly where the responsibility sits. When ownership isn’t explicit, every expansion of autonomy is a leap of faith.
Accountability is the infrastructure of ambition
Governance must be part of the enterprise AI infrastructure. It cannot be effectively backfilled after agents are already making decisions, touching sensitive systems or operating across critical workflows. Leaders need to define the rules of governance now: what agents can do, where human review is required, how actions are monitored and who is accountable for the outcome.
AI agents will transform how work gets done. The enterprises that realize that potential first won’t be the ones that moved slowest or the ones that moved recklessly. They’ll be the ones that built accountability into the foundation, so they could hand their agents real work and hold nothing back.