Enterprises spent the last two years teaching AI agents to reason. Getting those agents through the front door of the open web is the harder problem in 2026. Gartner expects more than 40% of agentic AI projects to be scrapped by the end of 2027, blaming cost, unclear value, and weak controls. One cause rarely makes it into the post-mortems: the agent worked in the pilot and then got blocked the moment it touched a live site.
That failure is not a model problem. It is an access problem, and it is getting worse on purpose.
The Open Web Is Starting to Refuse Agents
Even before agents, the web was hostile to automation. Bad bots made up 37% of all internet traffic in 2024, and automated traffic crossed half of the total for the first time on record. Defenses tuned to that reality do not stop to ask whether the automation on the other end is a scraper or a helpful assistant acting for a paying customer. They see a non-human client and challenge it.
Now the default itself is shifting. In September 2026, Cloudflare moved to block AI crawler and agent traffic by default across a large share of the sites it fronts, turning what used to be an opt-in restriction into the standing policy. A site owner no longer has to lift a finger to keep agents out. They are out unless someone explicitly lets them in.
This is why AI agents get blocked even while doing legitimate work, and why so many are now blocked by Cloudflare before a request ever reaches the site: the web treats unknown automation as guilty until proven otherwise.
Separating the three ways a block actually lands helps, because each needs a different answer. A policy block is the site or its network refusing the agent category outright, no matter how clean the traffic looks. A bot flag is a detection system scoring the connection as automated and then challenging or dropping it. A rate limit, the 429 response, can come from the target site or from your own model provider’s API, and those two have nothing to do with each other. Only the middle one is really about disguise, so only the middle one is solved by looking more like a real user.
For that bot-flag case, the mechanics are blunter than the headlines. Most agents are not banned outright; each one gets flagged as a bot instead. They run from datacenter IP ranges that score as high risk, on headless browsers that leak automation markers, with fresh profiles that carry no cookies or history and a TLS fingerprint that does not match the browser they claim to be. Everything about the connection reads as a throwaway script, so the site treats it like one. Its reasoning engine never gets a turn.
A common reflex makes this worse. Teams rotate through a large pool of IPs to look less repetitive, but rotating mid-task shreds the session continuity that makes an agent look like one consistent person, so the trick meant to dodge blocks ends up causing them.
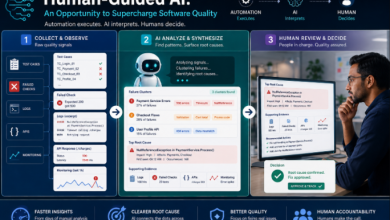
Picture a procurement agent that compares supplier prices, or a travel agent that books across a dozen portals. In a demo it works. In production it hits a login wall, a verification prompt, or a silent block on the third site, and the whole workflow dies there. Intelligence was never the bottleneck. The connection was.
The Fix Is Identity and Infrastructure, Not a Bigger Model
So how do you fix an AI agent that keeps getting blocked? Not with a smarter model. The fix is giving the agent a legitimate presence on the network: a stable identity it holds across a whole task, an IP that belongs to a real consumer network rather than a server farm, a way to receive a verification code when a service demands one, and approved spending when it has to transact.
Each of those maps to a specific failure above. A consumer-grade mobile IP answers the datacenter-reputation problem, because traffic from a real carrier network carries a trust score a hosting range never will, and because many real users share one carrier address, a site cannot blanket-ban it without hitting its own customers. One identity held for the length of a task answers the session-continuity problem that rotation breaks. A real phone number, ideally non-VoIP, answers the verification wall, since a growing share of services gate signup and login behind an SMS code that a disposable number cannot reliably receive.
This is where the Model Context Protocol, or MCP, earns its place beyond the hype. It standardized how an agent calls external tools, so capabilities that used to demand custom plumbing now arrive through one interface. An agent can request a real mobile IP, a phone number, or a data plan the same way it calls any other tool, with a human kept in the loop on anything that costs money.
Infrastructure providers are forming around exactly this gap. VoidMob, for one, gives agents real mobile IPs, non-VoIP numbers, and eSIM data through an open-source MCP server and through direct integrations with the antidetect browsers and cloud phones many teams already run. Purchases draw from a prepaid balance with per-order caps and human approval, so an autonomous agent can act without an open-ended claim on the budget, and keys can be scoped per agent and revoked on the spot. It is one example of a pattern taking shape across the market: a real-network identity provisioned over a protocol. (Disclosure: VoidMob operates this infrastructure.)
Controls matter as much as access here, especially for anyone answering to a security team. An agent that can spend money needs a ceiling it cannot exceed, an approval step on anything meaningful, and credentials that can be pulled the instant something looks wrong. Those guardrails are what move an agent from a risky science project to something a company can actually run in production, and they are usually missing from the pilots that later get cancelled.
None of this is about helping bad bots hide, just the opposite. It lets a legitimate agent present as what it actually is, a real user acting for a real person, so the defenses built to stop abuse stop catching the traffic that was never the threat.
What This Means for the Next Two Years
Enterprises that get real value from agents will not be the ones with the biggest model. They will be the ones whose agents can actually reach the systems the work depends on, with an identity that holds up and controls a security team will sign off on. The reasoning layer is close to solved. The access layer is where the next two years of agentic AI get won or lost.
So the question for any leader running an agent pilot right now is a simple one. When your agent leaves the lab and knocks on a real door, does anything open?