Software developed for highly regulated industries and mission-critical applications cannot be released just because it appears to work. Organisations have long been required to demonstrate that changes comply with policy (internal or external), that sensitive systems remain protected, that quality thresholds have been met, and that every release has a fully accessible history of the decision-making process and supporting evidence. Add AI into the mix and the stakes reach a whole new level. AI not only creates more artefacts and takes actions at an unprecedented pace and scale, but its inherent ‘black box’ nature makes control, visibility, and traceability even more challenging.
Understandably, for many organisations in highly regulated or mission-critical markets, this has naturally led to a risk-averse attitude to AI adoption. AI in these enterprises may be restricted to limited internal pilots and lower-risk workflows, rather than deployed at scale across core operations and market-facing applications. Yet caution can come at the risk of being left behind, being seen as lacking in innovation, losing competitive advantage or watching customers choose to go elsewhere.
There does not have to be a trade-off between control and governance versus speed and agility in these applications and markets. I would argue that the former contributes to the latter. In an AI-driven development lifecycle, better control can be what makes speed sustainable, especially as the volume of AI actions and artefacts continues to explode.
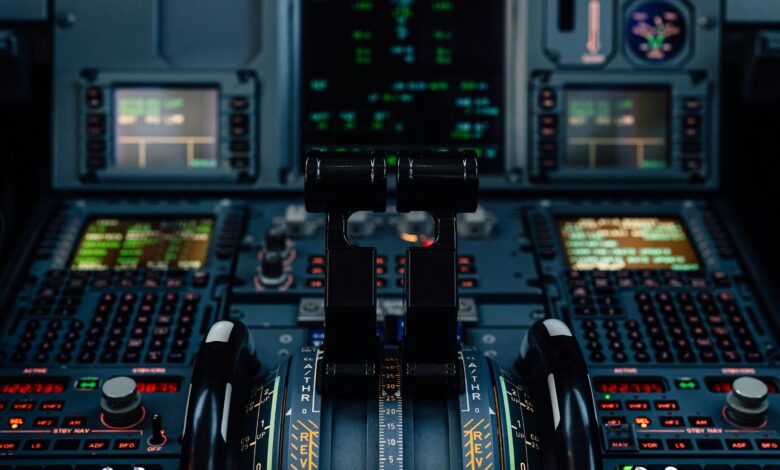
Humans-in-the-loop remain essential, especially in these environments where the consequences of something going wrong are so serious, but they are not enough on their own. Human-paced change and observation cannot keep up with the accelerating velocity and scale that agentic AI supports. Instead, humans become the gatekeepers, who have the expertise and experience to scrutinise and challenge AI’s outputs. Beneath this level of human supervision must sit a framework of technologies: think of the cockpit dashboard of a jumbo jet. The pilot does not need to know how all the technologies on the dashboard work, only interpret and guide them. Some of the critical capabilities that matter most to productionise AI includes centralised control over agents, autonomous testing that generates quality evidence as software is built, and continuous compliance.
Centralise Control Before Agents Multiply
Deploying a common governance layer reduces the friction of connecting agents, models, and data sources individually, while consistent access controls and secure credential management let teams introduce new AI capabilities fast. Rather than slowing innovation, these controls remove the fragmentation and uncertainty that otherwise create rework and delays, while also reducing unnecessary token costs and providing greater budget predictability.
An example use case might be a bank or healthcare organisation using several AI agents across code, testing, data and infrastructure, connected through both internal and third-party tools through Model Context Protocol (MCP) endpoints. A centralised “gateway” could provide one place to collaborate, manage credentials, permissions, policies, and activity, preventing each connection from becoming a separate governance and audit gap.
Move from Test Scripts to Autonomous Testing
The same principle of using AI for software building can be applied to testing that is an area of the software delivery lifecycle that has long been viewed as a bottleneck. While huge strides forward have been made in test automation over the past decade, many would argue that it has not been delivering the anticipated benefits. There are multiple factors involved in this plateau, but these become history once AI is applied to autonomous testing. This is far more than applying an AI interface; it is a whole new way of approaching this fundamental part of DevOps.
The latest innovations in testing shift the model from separate, specialist-managed scripts towards a ‘describe, execute, analyse’ workflow. A tester, business analyst or product team describes the outcome to be validated in natural language. AI then configures all the devices and environments involved, taking into account service-level expectations and schedules, before then orchestrating test execution across the board, together with the results.
Across web, mobile, and desktop environments, test validation can be extended to legacy applications that have traditionally been hard to automate, such as proprietary terminal-mainframe financial applications. This is because AI can reason over the visual interface and intended outcome, rather than depending on brittle object locators and scripts that break whenever something changes. The technology interprets and tests what it can see on screen across multiple screen types. New and legacy end-user environments are all brought into the same cohesive test framework, with one scenario that tests whether a service works correctly across all environments, rather than teams needing to create separate tests, manage handovers, or reconcile disconnected reports.
Elevate Compliance in the Agentic AI Era
For regulated and mission-critical applications in the era of agentic AI, compliance needs to receive a significant overhaul. It should become a continuous unified process that turns governance from a retrospective audit into an intelligent layer embedded across the software delivery lifecycle. This means that AI can be used as an intelligent translation layer between written policy and technical enforcement, using natural language to articulate instructions to AI, which then maps them to relevant regulatory frameworks, analyses their likely impact, and converts their intent into controls that can be applied across the relevant infrastructure.
Once deployed, AI then helps identify compliance drift, diagnose root cause and propose remediation through a pull request for an engineer to approve, after which the fix can be applied and verified automatically. This is essentially a step up from established automated continuous compliance processes, with the AI layer providing the connection between policy, analysis, remediation and giving mission-critical and regulated businesses the audit-ready evidence they need, in one continuous process.
An example use case might be an automotive or aerospace team applying policy continuously across code quality, safety, IP provenance and release workflows. Each code commit and artefact can be checked against the applicable rules, with violations stopped or escalated, and evidence captured automatically, creating a traceable compliance record from development through to release.
Governance, compliance, and quality become continuous enablers of delivery, with teams able to move faster because the necessary evidence, safeguards, and validation are being generated alongside the software, rather than steps added later in the software delivery lifecycle (SDLC).
The organisations that succeed with AI in highly regulated and mission-critical environments will be those that make innovation safe, visible and repeatable. By combining expert human oversight with centralised orchestration, continuous compliance and autonomous validation, teams can replace caution with justified confidence, and move AI from isolated experimentation into tangible benefits across the SDLC that support speed and innovation, without sacrificing control.