Reframing regulation
When OpenAI pauses deployment pipelines over safety concerns, and Anthropic warns that powerful AI could pose existential risks to humanity, no enterprise can assume AI safety has been pre-packaged. Every organisation that deploys AI inherits risk, regardless of who built the model. Navigating that liability is why regulation matters: far from stifling innovation, clear frameworks give enterprises the guardrails to scale with confidence. AI oversight is no longer a technical consideration to delegate – it is now the most significant governance priority for the boardroom.
Different rulebooks, one clear signal
AI regulation may currently look fragmented, but the global direction is consistent. The EU AI Act sets a risk-based regime with real penalties. The Central Bank of the UAE has issued guidance built on governance and accountability, fairness, transparency, effective human oversight and data management. It is non-binding, but it expects organisations to adopt a documented governance framework and keep human review central to critical decisions.
Beneath the differing legal jargon, expectations converge on four non-negotiables: transparency, accountability, human oversight, and proactive risk management. Regulators expect institutions to explain how AI reaches decisions that affect customers. They want firms to know where AI is being used, understand the risks it creates, and show how those risks are governed, monitored and controlled. For banks, insurers and other financial institutions, that scrutiny is now a current and active commercial reality.
A shift in responsibility
This changes who owns AI risk. It can no longer sit with a technology team that reports once a quarter to executive leadership. Technology, risk, compliance, legal, and commercial heads each hold a piece of the answer, and none can evidence compliance in isolation.
In practice, this means shared accountability now sits at board level. It also means a live inventory of the organisation’s AI footprint, agreed governance thresholds, and a unified evidence base that any function can substantiate under regulatory scrutiny. Organisations that keep these functions in silos will struggle to produce a timely and coherent answer when asked for proof by regulators.
Why yesterday’s tools fall short
Most governance and risk tooling was built for a slower world. It assumes a system is validated, signed off and then changes only occasionally, with risk captured in periodic assessments, spreadsheets and policy documents.
Modern AI does not behave that way. Models drift, third-party vendors update them without warning, prompts evolve and autonomous agents act across live systems. A point-in-time review tells regulators very little about what a system is doing today. What boards now need is continuous visibility: a current registry of every active AI model, automated monitoring, change controls integrated into deployment, and evidence that can be produced on demand.
Human oversight has to be meaningful
“Human in the loop” is one of enterprise AI’s most abused phrases – it’s easy to claim and hard to evidence. Meaningful oversight means the reviewer can evaluate the model’s rationale, has enough time and information to assess it, and has the authority to challenge and override the system. A person clicking approve on a queue of machine recommendations doesn’t meet that standard.
For the finance sector, this particularly matters in high-impact decisions such as lending, underwriting, fraud detection and claims processing. Institutions must be able to show who reviews which decisions, on what basis, and what happens when a reviewer disagrees with the model. They must also record these interventions, because the record is the evidence.
The reclassification nobody noticed
Regulatory drift is enterprise AI’s quietest liability: legal obligations can change without anyone consciously deciding it should. Take a standard deployment: an organisation uses an off-the-shelf model to summarise job applications for a recruiter. This is a deployer relationship with straightforward obligations. But then comes a shift: the engineering team fine-tunes the model on internal hiring data to automatically shortlist applicants.
Just like that, the statutory line is crossed – recruitment is an explicit high-risk use case. Under the EU AI Act, altering a system’s intended purpose strips away deployer status and legally reclassifies the organisation as a provider. The organisation now becomes responsible for a quality management system, technical documentation, conformity assessment and registration in the EU database. An ordinary product decision, taken without considering the compliance implications, has rewritten the company’s legal exposure.
The same mechanism takes other forms. Putting your own brand on a vendor’s model or removing a human approval step during a platform migration, can have the same effect. The high-risk deadline has moved to December 2027, but the role change happens the day the decision is made, and so does the exposure.
Inaction is an active liability
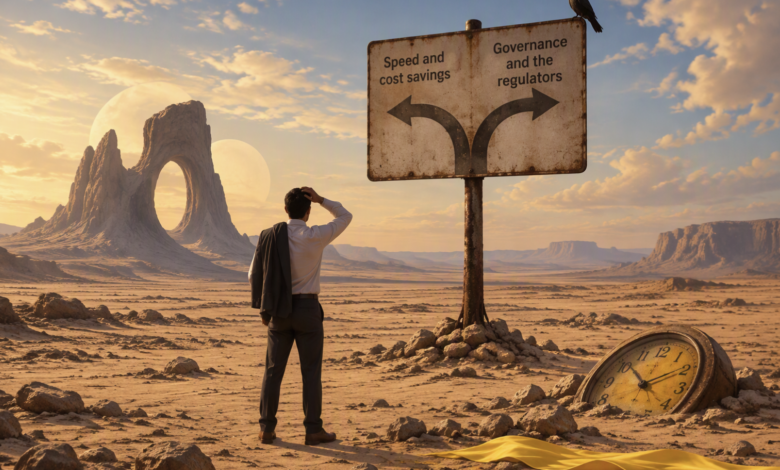
Delay is a choice with a price. Transparency obligations are already binding, further bans take effect this December, and enforcement powers are active. Fines for the most serious breaches run to tens of millions of euros or a percentage of global turnover.
Regulators are unlikely to start with the technically complex cases. They will go first for failures that are clear and easy to evidence: no AI inventory, no named owner, no logs, no record of human review. Organisations that defer action will face a chaotic, expensive scramble to build compliance under regulatory pressure, when the same framework built now could be steady and deliberate.
Three moves to make now
Having worked with banks and insurers across the US, Europe and the Middle East, I’ve seen a common pattern emerge: organisations often focus on the sophistication of their AI models but pay less attention to the governance processes needed to manage them effectively.
In practical terms, there are three steps I recommend. First, build an AI inventory with a named owner for every system, including third-party and embedded models. Second, add a role-change trigger to the change process so that every fine-tune, rebrand or workflow change prompts the question of whether it alters the organisation’s obligations. Third, evidence human review for high-impact decisions, including who reviewed, what they saw and when they overrode the model.
None of this requires perfect regulatory clarity. It requires ownership, discipline and a process that runs before the product ships.
Governance by design
The most successful organisations I’ve worked with treat governance as a design principle, built into how AI is selected, changed and monitored. For them, guardrails become an accelerant rather than a brake. Their teams move faster, because they know where the boundaries are and can prove they have stayed within them.
Many of the EU AI Act’s detailed technical standards are still years away, and waiting for perfect clarity is not a strategy. From my perspective, the priority is to build the capabilities, expertise, processes and oversight mechanisms that can absorb new requirements as they emerge. The enterprise AI race will not be won by those who scale recklessly; it belongs to those who test their governance before a regulator does.