One of the hardest failures to detect in production machine learning makes no noise. The service stays online, requests receive answers, and infrastructure dashboards show no obvious problem. Yet the predictions become less useful as the conditions surrounding the model change.
This gap between service availability and predictive reliability creates a demanding engineering problem. Organizations need to understand whether an AI application is running correctly, whether its outputs remain useful and whether someone can deliberately manipulate its behaviour.
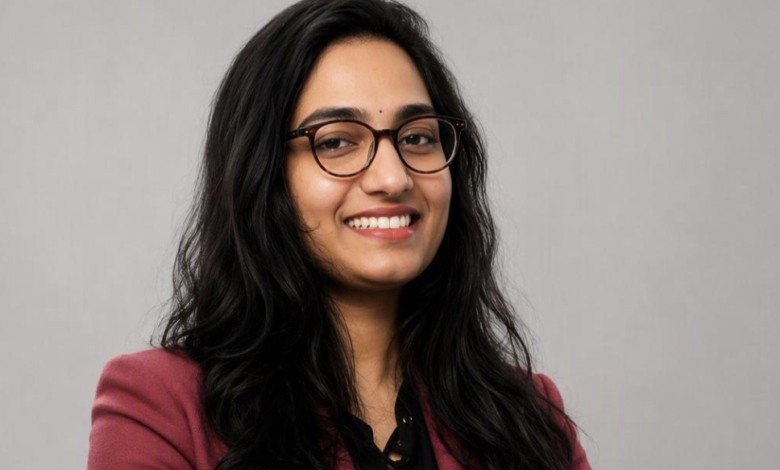
Dedeepya Yarra’s work connects cloud-based machine-learning operations with research into adversarial attacks and AI-based intrusion detection. These areas address complementary aspects of dependable AI: maintaining the systems that support models and examining the conditions under which their outputs can become unreliable.
Looking Beyond System Availability
Conventional monitoring tracks concerns such as outages, response times and resource consumption. Machine-learning applications require additional attention because their behaviour also depends on data, feature processing and model versions.
A change in incoming data can affect predictions without triggering an application error. Changes in prediction patterns may signal a problem, although determining whether accuracy has declined often requires access to verified outcomes.
Effective monitoring therefore needs to connect operational signals with model evaluation. Detecting a shift is the beginning of an investigation: teams must determine what changed, whether it matters and what response is appropriate.
This distinction provides an important context for Yarra’s MLOps focus. Managing a deployed model involves understanding both its execution environment and the evidence needed to assess its continued usefulness.
Making Deployment Repeatable
Investigating unreliable results becomes harder when deployment environments are inconsistent. Differences in dependencies, configuration settings or infrastructure can obscure the source of a problem.
Yarra’s experience with containerization, Kubernetes and infrastructure automation relates to this challenge. Containers package applications with their dependencies, supporting greater consistency between environments. Kubernetes coordinates containerized workloads, while Infrastructure-as-Code provides versioned definitions of the resources supporting them.
Automated delivery workflows connect these components through defined testing and release stages. For machine-learning applications, those stages may also need to account for model artifacts, evaluation results and data checks.
The practical value is traceability. When an application changes, teams need a clear record of what was released and the conditions under which it was evaluated. That record helps distinguish a deployment issue from a change in model behaviour.
Examining Deliberate Manipulation
Changing operating conditions are only one source of unreliable predictions. An attacker may intentionally construct inputs that cause a model to produce an incorrect result while the surrounding application continues to function.
Yarra’s research into adversarial machine learning examines black-box and white-box attack techniques. Black-box settings involve limited knowledge of or access to the model, potentially including its predictions or confidence scores. White-box settings provide access to internal information, such as model parameters or gradients.
Studying these settings helps investigate how vulnerabilities vary with an attacker’s knowledge. It also highlights a limitation of conventional health checks: a responsive service can still produce an output that has been deliberately manipulated.
Her work involving machine-learning-based intrusion detection examines the complementary application of AI to identifying malicious activity. Together, these research areas connect the protection of intelligent systems with their use in cybersecurity.
Bringing Model Security into Public Discussion
As a panel member during the University of North Texas Cyber Security Month, Yarra discussed adversarial attacks and their cybersecurity implications.
The subject connects model research with practical questions about deployment. What access should an application permit? Which inputs require scrutiny? How should teams evaluate behaviour that falls outside expected conditions?
Her participation brought these AI-specific concerns into a wider cybersecurity discussion. It complements her technical work by drawing attention to risks that cannot be assessed solely through infrastructure availability or conventional software testing.
Connecting Reliability and Security
Production AI requires several kinds of evidence: that an application runs consistently, that its predictions remain useful and that its behaviour has been examined under relevant threats. Each answers a different question about whether the system can be depended upon.
Yarra’s work brings the security of model behaviour into the same discussion as the reliability of the systems supporting it. That connection addresses a central challenge of operational AI: recognizing when a functioning application is no longer producing results that deserve trust.