Between March 2025 and February 2026, American companies hit by a data breach paid an average of $11.50 million to deal with it. Across every country in the study, the average was $4.99 million. The $6.51 million between them is the widest yet, and a three-year comparison of US and global breach costs shows that nearly all of the widening came from the American side. US companies are now paying $2.14 million more per breach than they were in 2024. The global figure has moved by $0.11 million.
The numbers come from IBM’s annual Cost of a Data Breach study, which the Ponemon Institute runs on IBM’s behalf. For the 2026 edition, published at the end of July, researchers followed 602 breached organizations and interviewed more than 3,550 of the security staff and executives who dealt with those breaches. Its global average is a record, up 12% after a dip in 2025, when companies were finding and containing breaches faster and paying less as a result.
American companies never saw that dip, and their average went from $9.36 million in 2024 to $10.22 million in 2025, while breaches elsewhere were getting cheaper before climbing again this year.
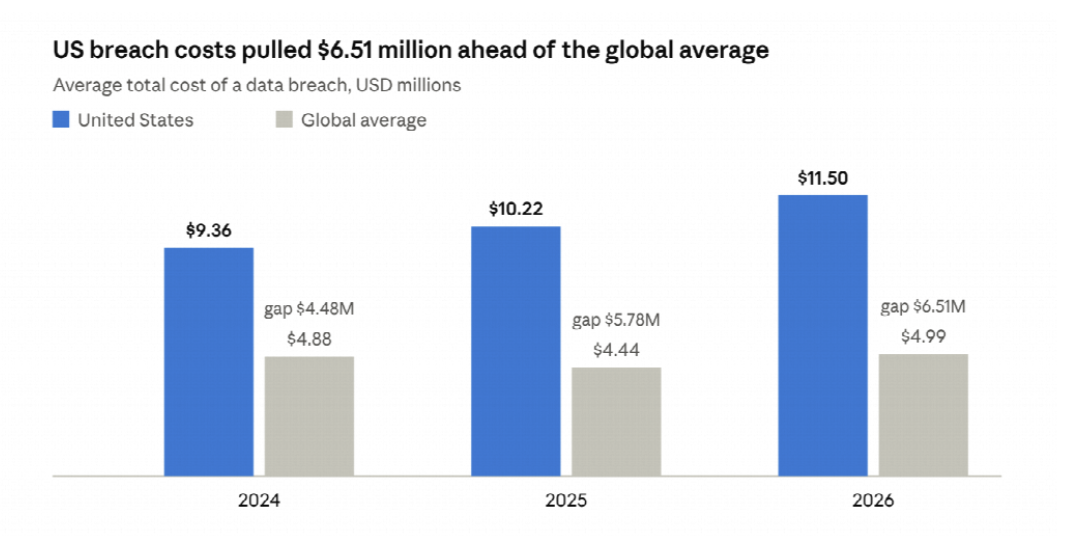
Source: IBM Cost of a Data Breach Report, 2025 and 2026 editions (2024 US figure as published in the 2025 edition)
IBM’s explanation for the American premium is brief. Business costs are higher in the US, and so are regulatory fines, as Insurance Journal reported when the study came out. In practice that short answer covers a lot. A US company has to work through notification rules that differ from state to state, pays outside counsel and forensic investigators at American rates, and often faces a class action within weeks of telling customers what happened.
The country tables show how far ahead the US is. The Middle East had the next highest average at $8.00 million, which still leaves it $3.50 million behind. Canada came in at $5.20 million. The UK average barely moved, to $4.17 million, so a typical British breach cost a little over a third of a typical American one. Healthcare, which has topped IBM’s industry ranking for years, averaged $6.64 million worldwide. An average US breach in any sector cost far more than that.
Slow detection makes the gap more expensive. The average breach took 247 days to find and contain in the 2026 study, up from 241 and the first increase in five years. Breaches that ran past 200 days averaged $5.65 million, against $4.32 million for those closed sooner. Suja Viswesan, a vice president in IBM’s security software business, said the lag between discovery and remediation “shows up directly in breach costs.” For a US company, those extra weeks add to a bill that already starts at more than twice the global level.
Some of the spending that cuts that time is now measurable. Organizations that used security AI and automation extensively averaged $4.00 million per breach worldwide, compared with $5.93 million for those that used none, and they closed breaches 65 days faster. Only 36% of the companies in the study were in that first group. Attackers are using the same technology: IBM counted 56% more AI-driven attacks than a year earlier, and breaches involving them cost roughly $1 million more than the average.
The practical problem belongs to whoever sets the budget. The global headline has stayed between $4.44 million and $4.99 million for three years and looks manageable on a slide. Any cyber insurance limit or incident-response reserve sized against it would cover less than half of what an average American breach now costs. A company that priced its cover in 2024 off the US figure of the time, $9.36 million, is already about $2 million behind.