At the moment two vehicles collide, a company truck is already recording. The dashcam is holding the last few minutes in a loop, the engine control module is logging speed and brake pressure, the telematics unit is pinging GPS, and the electronic logging device is timestamping the driver’s duty status. In the span of a heartbeat, all of that operational data quietly becomes something else: legal evidence.
Here is the problem most businesses never see coming. That evidence is on a countdown. The dashcam loop will overwrite itself in hours or days, the telematics history will age out of the vendor’s retention window, and unless someone deliberately intervenes, the single most important record of what happened will be gone before anyone thinks to look for it not through sabotage, but through the normal, automatic operation of the systems that captured it.
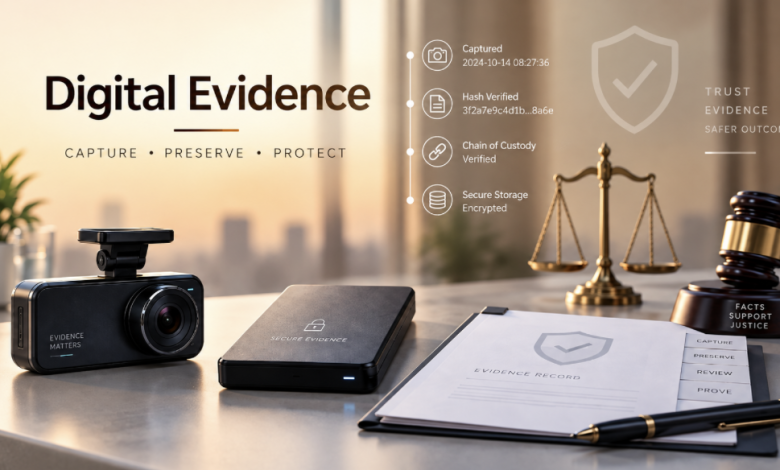
A digital evidence policy is what turns that fragile, self-erasing data into something that survives, holds up, and can be produced when it matters. This article treats that policy as a technical pipeline to capture, preserve, authenticate, retain, produce and walks through where it breaks and how to build it so it doesn’t.
Why “We Have Dashcams” Isn’t a Policy
Buying hardware is the easy part, and it lulls companies into thinking the problem is solved. A fleet can be fully wired with cameras and telematics and still lose every dispute, because capturing data and having usable evidence are two entirely different things separated by governance.
The gap shows up in predictable places. The footage exists but was overwritten before anyone preserved it. The clip survives but has no verifiable timestamp, so its authenticity is challenged. The data is intact but locked inside a vendor’s platform nobody can reach. Each is a governance failure, not a hardware one, and no amount of additional cameras fixes it.
The useful way to think about it is as a pipeline: data has to move successfully through five stages before it counts as evidence, and a break at any stage discards everything downstream.
| Stage | What it does | Where it fails |
| Capture | Record the right data at usable quality | Wrong settings, low resolution, short buffer |
| Preserve | Stop deletion once an incident occurs | Auto-overwrite, no legal hold triggered |
| Authenticate | Prove the data is genuine and unaltered | No hashing, no timestamp, broken custody |
| Retain | Keep it for the legally required period | Deleted too early, or kept forever as new risk |
| Produce | Retrieve and hand it over on demand | Data siloed in an unreachable vendor cloud |
The Data You Didn’t Know You Were Collecting
Most teams picture “evidence” as dashcam video and stop there. A modern commercial vehicle generates a far richer record, and the strongest cases combine sources that corroborate each other rather than relying on footage alone.
It’s worth knowing what each source actually proves, because that determines what your policy has to protect:
- Dashcam footage is the human-readable account of the seconds around a crash, and often the first thing a jury wants to see. Dual-facing units also capture the driver, which cuts both ways depending on what they were doing.
- The electronic logging device (ELD) federally mandated on most commercial vehicles, it timestamps duty status and driving hours, and establishes whether a fatigued driver was over their legal limit. Carriers must retain ELD data for at least six months.
- Engine control module and event data recorder the vehicle’s own black box, logging speed, throttle, brake application, and steering in the seconds before impact. This is machine data that’s hard to dispute and frequently contradicts eyewitness memory.
- Telematics and GPS the continuous track of where the vehicle was, how fast, and on what route, which can confirm or demolish a claim about location and timing.
- ADAS and safety-system logs whether forward-collision or lane-departure warnings fired and whether the driver responded, which speaks directly to the standard of care.
- Dispatch, routing, and maintenance systems the surrounding context: what the driver was told to do, whether the brakes were serviced, whether the schedule created pressure to speed.
A policy that protects only the dashcam and ignores the other five is protecting the least authoritative source while letting the machine data expire.
Capture: Getting the Data That Actually Matters
Capture sounds trivial the device is on, it’s recording but default configurations routinely lose the exact clip that matters. The culprit is loop recording: to save storage, most dashcams continuously overwrite the oldest footage, so a crash recorded on Monday can be gone by Wednesday if nothing flags it.
Event-triggered capture is the partial fix. When an accelerometer detects a hard braking or impact event, the system locks that segment and often uploads it to the cloud, protecting it from the overwrite cycle. But this depends on the trigger firing correctly, and low-speed or unusual collisions sometimes don’t cross the threshold precisely when a manual preservation step becomes essential.
Quality settings decide whether the surviving footage is useful. Resolution that can’t resolve a license plate, a frame rate that blurs a fast sequence, or a retention buffer too short to hold the footage until someone acts each turns captured data into unusable data. These are policy decisions, not IT defaults, and should be set for the value of the evidence rather than the cost of the storage.
Preservation: The Legal Hold Nobody Triggered
If there’s a single point where companies lose cases they should win, it’s here. The duty to preserve evidence attaches the moment litigation is reasonably anticipated after a serious crash, immediately and from that point, letting your systems auto-delete on their normal schedule stops being housekeeping and becomes spoliation.
The technical reality collides with the legal one badly. Your retention automation is doing exactly what it was designed to do when it overwrites the dashcam loop or purges 90-day-old telematics; the law simply expects a human to intervene first with a legal hold that suspends deletion for the relevant data. When that hold never gets triggered, the evidence is destroyed by design.
The consequences scale with what the court believes about your intent, and they are worth understanding precisely:
| What happened | How courts treat it (FRCP 37(e)) | Practical effect |
| Data lost to routine auto-deletion, no hold | Sanctions if reasonable steps weren’t taken to preserve | Curative measures; credibility damaged |
| Loss causes real prejudice to the other side | Court may order measures “no greater than necessary” | Adverse rulings on specific facts |
| Intent to deprive the other party is found | The severe sanctions unlock | Jury told to presume the data was unfavorable; possible dismissal or default |
The technical nuance: under the 2015 amendment to Rule 37(e), the harshest sanctions an adverse-inference instruction telling the jury to assume the lost footage was bad for you require a finding of intent, and negligence alone doesn’t reach it. That is thinner protection than it sounds. “Our system deleted it automatically” invites a hard look at whether ignoring an obvious duty to preserve was really an accident.
Authentication: Proving the Footage Is Real
Surviving footage is only valuable if you can prove it’s genuine, and that proof is a technical property built at capture time, not a form filled out later. Opposing counsel will question whether a clip was edited, whether its timestamp is accurate, and whether anyone could have altered it in storage and “trust us” is not an answer.
The mechanisms are concrete. A cryptographic hash generated when the file is created acts as a fingerprint: if a single frame changes, the hash no longer matches, proving the file unaltered. Synchronized timestamps and embedded metadata (device ID, GPS coordinates, firmware version) place the footage at a specific time and place. Together these form a chain of custody, a verifiable record from creation to courtroom.
This has become more urgent, not less. As AI-generated and manipulated video grows harder to detect by eye, the ability to cryptographically demonstrate that a file is original is shifting from a nice-to-have to the baseline for admissibility. A policy that captures footage but can’t authenticate it is building on sand: the evidence that can’t be verified is the evidence that gets excluded.
When the Data Meets the Courtroom
The whole pipeline exists to serve one moment: a real dispute in which the data is the contested core. What happens to the evidence there shapes what the policy has to deliver.
In a serious commercial-vehicle collision, the volume and technical complexity of the data are high enough that it doesn’t interpret itself. Reconstructing the incident routinely brings in accident-reconstruction engineers working alongside a specialist San Luis Obispo truck accident attorney, who work from the same event-recorder data, ELD records, telematics, and video the company’s own systems captured. The evidence a business preserves is the raw material both sides build their case from.
This is why the pipeline’s integrity matters so much downstream. Clean, authenticated, well-retained data can establish precisely what happened and shut down a weak claim quickly; gaps, unverifiable timestamps, or conveniently missing footage do the opposite, and a jury tends to fill an unexplained absence of data with the least charitable assumption. Governing evidence well isn’t just self-protection; it keeps the factual record complete enough for the dispute to be resolved on what actually occurred.
Retention: How Long, and Who Decides
Once data is preserved and authenticated, the next question is how long to keep it and the answer is genuinely hard, because the pressures pull in opposite directions. Keep data too briefly and you destroy evidence you were obligated to hold; keep everything forever and you create a growing archive that is itself a liability, discoverable and breachable.
The floor is set by law and it’s higher than many assume. ELD records carry a six-month federal retention minimum, and other categories maintenance, dispatch, insurance-related records carry their own schedules that often outlast the raw video. A retention policy has to reconcile these overlapping minimums rather than apply one blanket number, because the shortest retention window in your stack is the one a plaintiff will target.
The resolution is a tiered schedule keyed to evidentiary value and legal requirement: incident-flagged footage held for years, routine footage cycled in weeks, telematics and ELD data kept to their mandated minimums, everything under an automated hold the instant an incident is logged. “How long” is a deliberate risk decision, not a storage-cost default.
The Access Problem: Vendor Clouds and Data Silos
Evidence you technically own but cannot reach is evidence you don’t have. Most fleet data now lives in third-party platforms: the dashcam vendor’s cloud, the telematics provider’s portal, the ELD supplier’s servers and that dependency creates failure modes that surface at the worst possible time.
The problems are practical and common. Export tools that only produce low-resolution clips or PDF summaries rather than the original authenticated files. API rate limits that make pulling a large volume of footage slow or incomplete. Retention windows set by the vendor’s default plan rather than your legal needs, quietly deleting data you assumed was safe. And the sharpest one: switching or losing a telematics vendor and discovering the historical data doesn’t come with you.
A policy has to treat this as an integration and ownership question, negotiated before an incident: confirm in the contract who owns the data, how fast and in what format it can be exported, how long the vendor retains it, and what happens to the archive at offboarding because the moment you urgently need three-month-old footage is the wrong moment to learn the vendor purged it at 60 days.
Privacy and the Surveillance Tightrope
A digital evidence policy collects a lot of data about employees, and that pulls against a second set of obligations the policy has to hold in balance. Inward-facing cameras, continuous location tracking, and driver-monitoring systems generate exactly the evidence that wins cases and exactly the data that triggers privacy law.
The constraints are real and vary by jurisdiction. Several U.S. states regulate biometric data captured by driver-facing cameras, employee-consent requirements differ from place to place, and any operation touching the EU inherits GDPR’s rules on how long personal data can be held and for what purpose which can directly conflict with a long evidence-retention schedule.
The workable path is proportionality and transparency: collect what genuinely serves safety and evidence, tell drivers what’s recorded and why, restrict footage access to those who need it, and align retention with both legal minimums and privacy maximums. A policy that treats surveillance as unlimited invites its own liability, and driver resentment tends to sink the program before any lawsuit does.
Automating the Policy: From PDF to Pipeline
A policy that lives only in a document fails at the one moment it’s needed, because it depends on a stressed human remembering to act in the chaotic hours after a crash. The stronger approach is to encode those rules into the systems themselves, with AI evidence tools increasingly helping classify records, surface missing information, and connect related data before a human begins the deeper review.
In practice, that means wiring the pipeline to enforce itself. A few patterns carry most of the value:
- Automated legal holds, where logging an incident in the system immediately suspends deletion for that vehicle’s footage, telematics, and ELD data removing the dependency on someone manually flipping the switch in time.
- Retention-as-code, where the tiered schedule is enforced by the platform rather than by memory, so incident data is protected and routine data expires without anyone having to police it.
- Integration that consolidates evidence from cameras, ELD, and telematics into one place with consistent timestamps, so a crash doesn’t send staff scrambling across five vendor portals to assemble a timeline.
- Alerting that notifies the right people the instant a preservation-worthy event is detected, turning the critical first hours from a scramble into a defined, logged procedure.
The goal mirrors good engineering everywhere: make the compliant path the automatic one, so preservation doesn’t rely on heroics under pressure.
Building Your Digital Evidence Policy
Pulling the pipeline together, a workable policy is less a legal document than an operational specification. At minimum it should state:
- Which data sources are captured and at what quality naming the dashcam, ELD, event recorder, and telematics explicitly rather than assuming “the system” covers it.
- What event triggers a preservation hold, and exactly what that hold suspends, so deletion stops automatically the moment an incident is recorded.
- How each category of data is authenticated and how its chain of custody is maintained from capture to production.
- A tiered retention schedule that reconciles legal minimums, privacy maximums, and evidentiary value, with an owner accountable for each.
- Contractual data-access terms with every vendor ownership, export format, retention, and offboarding confirmed before the platform becomes load-bearing.
- Who is notified and what they do in the first hour after an incident, written down before it’s needed rather than improvised when it is.
None of these require a law degree to begin. They require treating digital evidence as a system to be designed, with clear owners and automated enforcement, rather than a pile of footage nobody has organized.
Final Thought
An accident involving a company vehicle is, over a long enough horizon, close to inevitable. Losing the evidence of what happened is not that’s a choice, usually made months earlier in a retention setting nobody revisited or a vendor contract nobody read closely.
A digital evidence policy is what separates the two outcomes. It turns a collection of self-erasing data streams into a reliable record that survives, authenticates, and can be produced on demand by treating evidence the way good teams treat any critical system: captured deliberately, preserved automatically, and governed long before the moment it has to hold up.